Ask most vendor websites where ISO 27001 requires your data to live and you will get a confident answer. Ask the standard, and you will get none. ISO 27001 Data Residency is not a requirement inside ISO/IEC 27001 at all — the standard is a management-system specification, and it is deliberately silent about geography. That matters commercially, because the obligation to keep data in a particular country almost always reaches you from somewhere else: a customer contract, a sectoral regulator, a financial services licence condition, or a privacy law's transfer rules. What ISO 27001 does give you is the machinery to make a location promise real and auditable — risk assessment, classification, supplier controls, cloud-service controls, logging and internal audit. This article explains how residency works inside an ISMS, what an auditor will ask you to show, and what an enterprise buyer is actually testing when they put the question in a security questionnaire.
ISO 27001 does not tell you where to store data
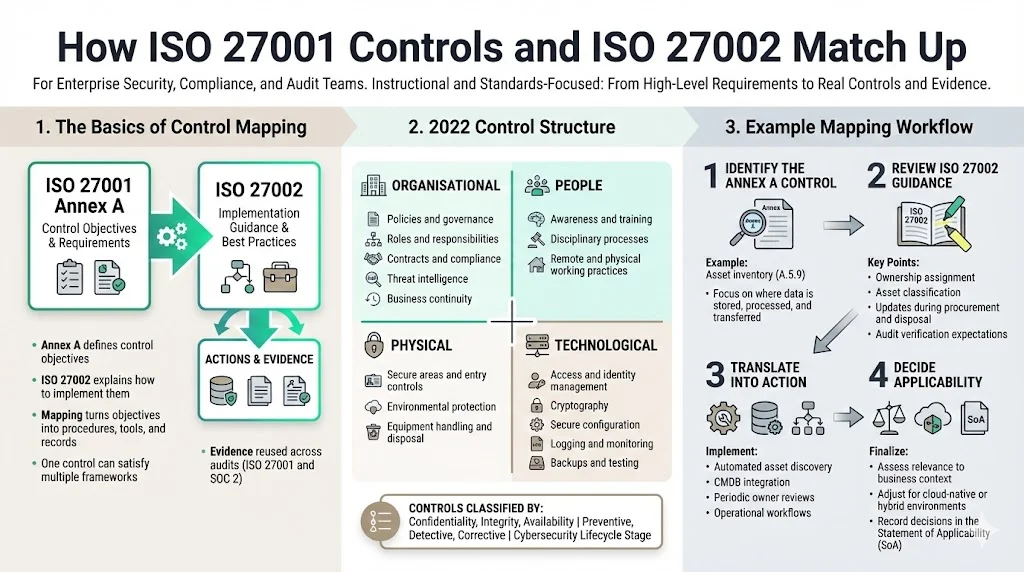
ISO/IEC 27001 does not tell you where to store data, and nothing in its requirements names a country, a region or a cloud zone. The standard sets out what an information security management system must do: establish scope and context, assign leadership and roles, assess and treat information security risks, resource and train the programme, operate controls, measure and audit them, and improve on findings. The 2022 revision pairs those requirements with Annex A, a reference set of 93 controls grouped into four themes — organisational, people, physical and technological. None of them mandates a storage location.
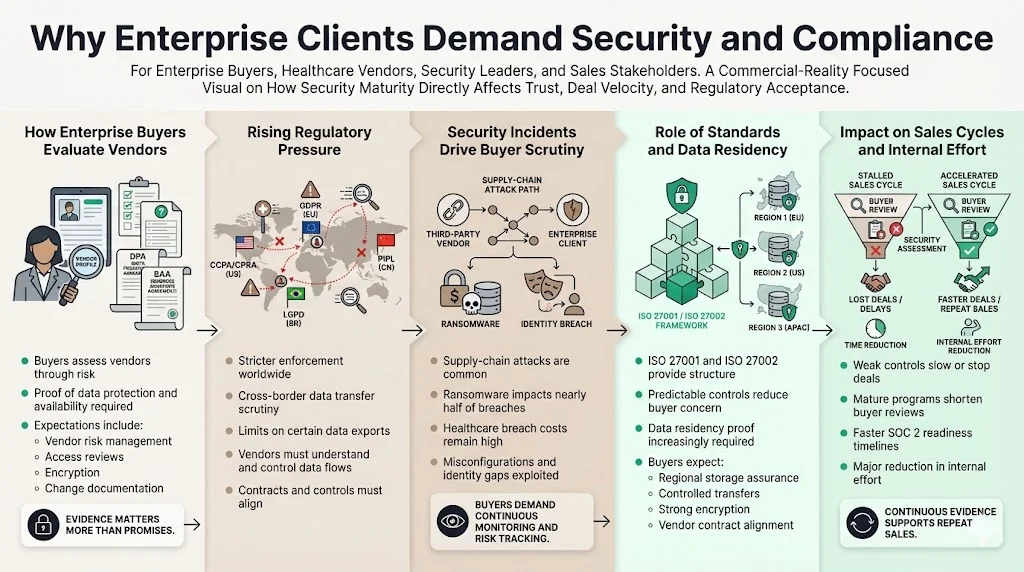
That design is intentional. ISO 27001 is written to be used by a two-person startup and a 40,000-person bank, in any jurisdiction, for any kind of information, so a geographic rule would have to be wrong for most of them. Instead of prescribing where information sits, the standard requires you to identify your legal, statutory, regulatory and contractual requirements and build the ISMS to meet them. If your contract with a German customer says their data stays in the European Economic Area, that commitment becomes an input the ISMS must honour — not because ISO said so, but because you said so and ISO requires you to keep track of what you said.
The practical consequence is a sentence worth learning verbatim for questionnaires and sales calls: ISO 27001 certification does not prove where your data is; it proves you have a system for knowing where your data is and controlling it. Conflating the two is how vendors end up with a certificate on the website and a residency commitment nobody can evidence. A scope statement covering three cloud regions tells a buyer the ISMS was audited across those regions. It says nothing about whether a fourth appeared last quarter when an engineer enabled cross-region backup replication. The same structural point applies to the sibling frameworks: SOC 2 data residency and HIPAA data residency are control frameworks too, not location laws.
Residency, sovereignty and localisation are three different obligations
Residency, sovereignty and localisation get used interchangeably in questionnaires, and the conflation causes real engineering waste. They are three distinct obligations with three different remedies, and separating them is usually the fastest hour of work in a residency programme:
-
Data residency is the physical location of the systems that store and process information — the cloud region, the data centre, the backup bucket. It is a factual, architectural property. You change it by changing configuration.
-
Data sovereignty is the question of whose law applies and who can lawfully compel access. Sovereignty does not follow the server alone: a US-headquartered provider operating an EU region may still be subject to US legal process under the CLOUD Act, which is precisely why sovereign cloud offerings and customer-held cryptographic keys exist. You change your sovereignty exposure by changing provider, governance model or key custody — not by moving a bucket.
-
Data localisation is a legal mandate that specified data must remain inside a border. It is the narrowest of the three and the only one that is genuinely non-negotiable where it applies. It typically attaches to particular sectors or data categories rather than to all personal data.
Most enterprise residency requirements are residency requirements in this strict sense: a contractual promise about location, enforceable by audit. A smaller number are sovereignty requirements, and those are the expensive ones, because they cannot be satisfied by a region setting. A very small number are true localisation mandates, and those are usually driven by a named regulator — a central bank's rules on payment data, a health regulator's rules on patient records, a public-sector procurement framework. Classifying each incoming requirement into one of the three buckets before you design anything will save a quarter of pointless architecture work.
Data location is a risk input to your ISMS
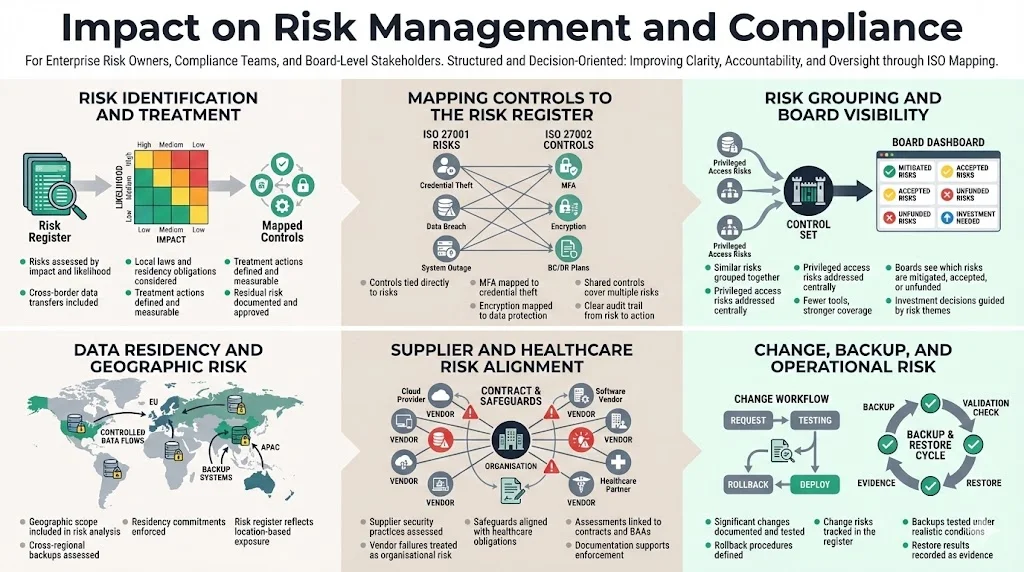
Inside an ISMS, data location is a risk input rather than a control. The risk assessment is where geography enters the standard, and treating it that way is what makes the rest of the programme coherent. For each information asset you already record what it is, who owns it and how sensitive it is. Residency simply adds two more attributes: where it currently sits, and where it is permitted to sit.
Once location is an attribute of the asset, several risks become assessable in the ordinary way:
-
Unlawful access by a foreign authority. A jurisdiction's legal process may compel a provider to disclose data regardless of where the hardware stands. The treatment is usually customer-managed keys, a sovereign or in-region operated service, or simply not placing that data class there.
-
Breach of a contractual commitment. You promised a customer their data stays in one region and a replica, log stream or support tool moved a copy elsewhere. This is the most common residency finding we see, and it is a control failure, not a legal one.
-
Conflicting legal duties. Two jurisdictions impose incompatible requirements on the same record — one demands retention, another demands erasure. The treatment is segmentation so the same record is never subject to both.
-
Latency and availability trade-offs. Concentrating data in one region to satisfy residency can weaken resilience. That is a real risk to accept consciously and document, not to discover during a regional outage. Our guide to ISO 27001 multi-region architectures covers the trade-off in detail.
Each of these gets a risk owner, a treatment decision and a review date, exactly like any other entry in the register. The Statement of Applicability is then where the connection becomes visible to an auditor: it records which Annex A controls you apply and why, and a programme with residency commitments should be able to point to the controls it leans on to keep those commitments. Writing the justification in terms of your own commitments — "applied; supports the EU-only storage commitment in our enterprise data processing agreement" — is far more useful to an auditor than a generic rationale.
The ISMS controls that actually govern where data sits
The ISMS controls that govern where data sits are not a single residency control but a handful of ordinary Annex A controls doing their normal jobs. Describing them by function rather than by identifier is also how you should write them in a questionnaire response, because a buyer's security reviewer cares what the control does:
| Buyer question | The part of the ISMS that answers it |
|---|---|
| Which data must stay in region, and how do you know? | The classification and labelling controls, plus the asset inventory that records each asset's permitted locations |
| Where does it currently sit? | The asset and configuration inventory, reconciled against cloud provider resource data rather than a spreadsheet |
| Who may move it? | The access control and change management controls, including who can create resources in a non-approved region |
| What stops an accidental transfer? | The information transfer controls and preventive guardrails such as region restrictions in cloud policy |
| How would you know if it happened? | The logging and monitoring controls, with alerting on resource creation and replication outside approved regions |
| Who else holds a copy? | The supplier relationship and cloud service controls, plus a maintained subprocessor register |
| Is the data protected if location fails? | The cryptography and key management controls, including where keys are held and who can use them |
Two observations matter more than the table itself. First, nothing here is specific to residency: if your access control, change management, logging and supplier management are weak, your residency commitments are weak, and no amount of residency-specific documentation fixes that. Residency is a stress test of the ISMS you already have.
Second, the preventive controls are worth disproportionately more than the detective ones. A policy document saying "production data is stored only in approved regions" is a statement of intent. A cloud organisation policy that denies resource creation outside those regions is a control. An auditor who has seen both will spend ten minutes on the first and ask for the configuration of the second. Pushing region restrictions into infrastructure-as-code and organisation-level policy is the single highest-leverage change in most residency programmes.
Supplier and cloud service controls decide what a processor may hold
Supplier and cloud service controls are where the residency question is really decided, because in a modern SaaS architecture most copies of customer data are held by somebody else. The 2022 revision of the control set made this explicit by adding dedicated guidance on the use of cloud services alongside the existing supplier relationship controls, and the companion standards — ISO/IEC 27017 for cloud service controls and ISO/IEC 27018 for personally identifiable information in public clouds — exist precisely to fill in the implementation detail.
In practice, a supplier control set that supports residency commitments does five things:
-
Records location per supplier, not per contract. Your subprocessor register should state, for each supplier, which data classes it receives and which regions it may hold them in. A register that lists vendors without locations cannot support a residency claim. ISO 27001 subprocessor management walks through building and maintaining one.
-
Puts the region in the contract. Data processing agreements should name permitted regions, require notice before a new region or subprocessor is introduced, and give you a right to object or exit. A supplier who will not commit to a region contractually cannot be part of a commitment you make to your own customer.
-
Bounds onward transfer. The supplier's own suppliers are your fourth parties. Flow-down clauses requiring equivalent location constraints are what stop a residency promise dissolving two tiers down the chain.
-
Checks capability before signing, not after. Many popular tools are single-region by architecture — particularly analytics, error tracking, session replay, support desks and AI features. Finding this out during a customer audit is expensive. Our ISO 27001 third-party risk guide covers the pre-contract assessment.
-
Reviews on a schedule. Suppliers change regions, acquire companies and add AI subprocessors between your annual reviews. A supplier review that only happens at renewal will be out of date.
The shared responsibility model deserves particular attention here, because residency sits awkwardly across it. The provider supplies the regional boundary; you are responsible for staying inside it. A provider offering nineteen regions has not given you a residency control — it has given you nineteen ways to break one. Our ISO 27001 shared responsibility model guide sets out which side of the line each obligation falls on.
Support and operational access is the blind spot. Customer data frequently does not move, but a support engineer in another country views it, exports a sample to a ticket, or takes a screenshot into a chat tool. If your commitment is about data residency and your reality includes global follow-the-sun support, you have either a scoping problem or a disclosure problem. Say which in the contract rather than hoping nobody checks.
International transfer duties arrive through contracts and privacy law
International transfer duties arrive through privacy law and customer contracts, never through ISO 27001 itself — and keeping that boundary clear is what stops a compliance programme from making promises it cannot defend. The ISMS is the delivery mechanism; the obligation originates elsewhere.
The main sources to track in 2026 are familiar. Under the GDPR, personal data may leave the European Economic Area only on a recognised legal footing — an adequacy decision for the destination country, Standard Contractual Clauses, Binding Corporate Rules or another approved mechanism — and since the Court of Justice's Schrems II judgment, organisations relying on contractual mechanisms are expected to assess the destination's laws and add supplementary technical measures where the contract alone is insufficient. The EU–US Data Privacy Framework restored an adequacy route for certified US recipients and remains under active legal challenge, which is why mature programmes keep Standard Contractual Clauses in place as a fallback. The United Kingdom operates its own transfer regime with its own instruments. India's regime is more permissive than most summaries suggest: the general position permits personal data to leave the country subject to government restriction, and the genuine localisation duty applies to organisations designated as significant data fiduciaries, for categories government specifies — see our DPDP cross-border data transfer guide.
For an ISO 27001 programme the work is not to re-implement privacy law but to make sure the ISMS knows about these obligations and can evidence them: the register of legal and contractual requirements lists them, each flow in the data map carries its transfer mechanism, the transfer risk assessments sit where an auditor can find them, and the supplementary measures those assessments named — encryption with keys held outside the destination jurisdiction, pseudonymisation, access restriction — are implemented and monitored rather than promised. The mechanics of each instrument are covered in ISO 27001 international transfers; if you process personal data at scale, ISO/IEC 27701 extends the ISMS into a privacy information management system and gives this work a structured home.
A residency promise is only as good as the control that enforces it.
Share your work email and we'll help you turn your region commitments into evidence an auditor and a buyer both accept.
Evidencing a residency claim for your ISO 27001 auditor
Evidencing a residency claim for your ISO 27001 auditor is a different exercise from describing it. Certification audits are conducted in two stages — a documentation review followed by an on-site or remote assessment of whether the ISMS operates as described — with surveillance audits in the intervening years and recertification on a three-year cycle. At each of those points, a residency commitment is tested as an operating control, not as a paragraph in a policy.
What a competent auditor asks for, in roughly the order they ask:
-
The commitment itself. Where is the residency promise written down? A customer contract, a trust page, a policy. If the auditor cannot find the commitment, there is nothing to test against — and a surprising number of programmes discover at this point that sales has promised something the ISMS has never heard of.
-
The data map. Which systems hold which data classes in which regions, including non-production environments, backups, logs, analytics stores, message queues and caches. Diagrams dated more than a year ago invite scrutiny of everything else.
-
Configuration proof, not screenshots. Infrastructure-as-code showing region constraints, organisation policy denying out-of-region resource creation, bucket and database region settings, replication settings explicitly disabled. Live exports beat screenshots because they are harder to curate.
-
Key custody evidence. Where cryptographic keys are generated, held and used, and who can use them. Data in an EU region with keys held and usable elsewhere is a weaker claim than it looks. ISO 27001 key management best practices covers the custody questions.
-
Monitoring and alert history. Evidence that out-of-region events would be detected, plus the record of any that were — including what you did about them. A clean monitoring record with no detections ever is less convincing than three detections with three documented responses.
-
Supplier register and contracts. The subprocessor list with regions, the data processing agreements, the most recent supplier reviews, and the transfer mechanism for each cross-border flow.
-
Internal audit and management review records. Residency should have appeared in at least one internal audit and one management review. Its absence suggests the commitment is not actually being managed.
-
Change records for region changes. Any new region added since the last audit should have a change record, a risk assessment and a customer notification where the contract required one.
The cycle matters here. A residency control added two weeks before a surveillance audit has almost no operating history, and an auditor will say so. Building the evidence continuously is the whole point: across more than 6,000 security audits, we consistently see that teams collecting evidence as a by-product of normal operations spend under 70 hours a year on audit work, against 550 to 600 hours when evidence is assembled retrospectively — and reach readiness in four to five months rather than nine to twelve. Our ISO 27001 evidence requirements guide lists what to capture and when.
What an enterprise buyer actually asks for
What an enterprise buyer actually asks for is narrower and more specific than most vendors prepare for. Security questionnaires ask "do you support data residency" as a yes/no, but the real diligence conversation that follows has about seven questions in it, and the quality of your answers determines whether the deal moves this quarter or next.
The questions, and what a good answer looks like:
| What they ask | What a weak answer sounds like | What a strong answer sounds like |
|---|---|---|
| Where will our data be stored? | "In the cloud, in your region." | Named region for primary storage, backups, logs and each subprocessor |
| Can we choose the region? | "We can look into it." | A stated list of supported regions, with the commercial and lead-time conditions |
| Where do backups and logs go? | Silence, or a confident answer that turns out to be wrong | Explicit per-system answer, including telemetry and error tracking |
| Who can access it from outside the region? | "Only authorised staff." | Named roles, the access path, whether support is in-region, and the logging of it |
| Who are your subprocessors and where are they? | A list with no locations | A maintained register with data classes and regions per supplier |
| What happens if you add a region? | Nothing documented | Contractual notice period, objection right, and the change process behind it |
| Can you prove it rather than assert it? | The ISO certificate | The certificate, the scope statement, the data map, and configuration evidence under NDA |
The last row is where ISO 27001 earns its keep. The certificate alone answers none of these questions, but an ISMS built to answer them produces the artefacts on request instead of starting a two-week internal scramble. Vendors selling to regulated buyers — a fintech under a licence condition about where payment data sits, a health technology company handling patient records, any vendor in a public-sector procurement framework — should expect these questions in writing and keep the answers in reusable form; our ISO 27001 customer security questionnaire guide covers building that answer library.
One piece of commercial advice: do not promise a region you have not built. Retrofitting a residency commitment after signature — migrating data, renegotiating subprocessor terms, splitting a single-tenant analytics pipeline — routinely costs more than the contract that triggered it was worth. A clear "we support these 3 regions today, and here is what adding a fourth would take" closes more deals than an optimistic yes.
Residency mistakes that surface in ISO 27001 audits
The residency mistakes that surface in ISO 27001 audits repeat with remarkable consistency, and all eight below are cheap to fix before an auditor finds them and expensive afterwards:
-
The commitment nobody told the ISMS about. Sales agrees to EU-only storage in a negotiated contract; the security team learns about it during the audit. The fix is a contract review step that routes residency commitments into the register of contractual requirements.
-
Primary storage in region, everything else not. Databases are usually configured correctly. Backups, read replicas, log aggregation, error tracking, product analytics, data warehouses, CDN caches and queue dead-letter stores are where copies escape.
-
Non-production environments holding real data. A staging environment in a different region loaded from a production snapshot breaks the commitment completely, and is one of the most common findings. Data classification is the control that prevents it.
-
Keys outside the boundary. In-region data with out-of-region key custody gives a sovereign-access exposure the region setting was supposed to close.
-
Policy without enforcement. A documented region restriction with no organisation policy or infrastructure-as-code guardrail behind it will be broken by an ordinary engineering decision within a year.
-
A stale subprocessor register. New tools get adopted faster than registers get updated, and AI features in existing tools frequently introduce new processing locations without any procurement event at all.
-
Support access treated as not a transfer. Viewing and exporting data from another country is a disclosure even when the storage never moved.
-
No detection. If the only way you would learn about an out-of-region copy is a customer audit, you do not have a control. Alerting on region-violating resource creation is a day of work. ISO 27001 continuous monitoring covers the tooling.
The pattern across all eight is the same: the residency story is accurate about the system people think about and wrong about the ones they do not. Enumerating every copy of the data — not every system, every copy — is the exercise that catches them.
Know where your data actually lives, not where you assume
Book a demo and we'll map every copy of your customer data against the regions you have committed to, then show you the controls and evidence that keep it there.
Book a demo
ISO 27001 Data Residency: Key Takeaways
ISO 27001 data residency comes down to five points worth carrying into your next buyer conversation. First, the standard mandates no location; certification proves you have a system for knowing and controlling where data sits, not where it sits. Second, residency, sovereignty and localisation are different obligations with different remedies, and misclassifying them wastes engineering effort. Third, location belongs in the risk assessment and the asset inventory as an attribute, which makes the ordinary controls — classification, access, change, logging, supplier management, cryptography — do the residency work. Fourth, transfer obligations come from privacy law and contracts, so the ISMS's job is to record them and evidence them rather than restate them. Fifth, enforcement beats documentation: a cloud policy that denies out-of-region resource creation is worth more than any number of pages saying it should not happen. Build the controls first and let the certificate describe something true.
ISO 27001 Data Residency FAQ
No. ISO/IEC 27001 is a management-system standard and specifies no storage location. It requires you to identify your legal, regulatory and contractual requirements and build the ISMS to meet them. Location mandates come from privacy laws, sector regulators and customer contracts — not from ISO 27001 itself.
No, and this is the most common misreading of a certificate. It shows that an ISMS covering the stated scope was audited against the standard. To establish location you need the scope statement plus the vendor's data flow map, region configuration evidence and subprocessor register with locations.
There is no single residency control. The work is carried by the classification and labelling controls, the asset inventory, access control and change management, the information transfer controls, logging and monitoring, cryptography and key management, and the supplier relationship and cloud service controls. Describe them by function in questionnaires rather than by identifier.
They arrive as inputs. GDPR transfer mechanisms such as adequacy decisions and Standard Contractual Clauses, UK instruments and other national regimes create the obligation; the ISMS records each obligation in the register of legal and contractual requirements, attaches a transfer mechanism to each flow in the data map, and evidences the technical measures the transfer assessment relied on.
Keep the written commitment, a current data map covering backups, logs and non-production environments, infrastructure-as-code and organisation policy showing enforced region constraints, key custody records, monitoring and alert history for out-of-region events, the subprocessor register with contracts, and internal audit and management review records that mention residency.
Both help with implementation detail rather than with location mandates. ISO/IEC 27017 gives cloud-specific control guidance and ISO/IEC 27018 addresses personally identifiable information in public clouds. ISO/IEC 27701 extends an ISMS into a privacy information management system, which gives transfer assessments and processing records a structured home.